AI Cybersecurity & Governance
Understand the evolving risks of generative and agentic AI and learn how to apply cybersecurity and governance frameworks to make informed decisions about AI adoption, security, and risk.
Modules/Weeks
Weekly Effort
Discipline
School
Format
Cost
Course Description
For a limited time, use promo code CYBER26 at checkout to enroll in this course for free! An optional $20 certificate is available for purchase upon course completion.
AI is no longer just answering questions. It is booking flights, reading email, interacting with other systems, and increasingly acting on our behalf. As AI shifts from passive assistant to autonomous agent, the opportunities are growing, but so are the risks.
AI Cybersecurity & Governance will help you understand what this shift means for cybersecurity, governance, and organizational decision-making. You will connect lessons from major historical data breaches to emerging vulnerabilities in generative and agentic AI, and understand how cybersecurity risks are evolving as AI systems become more capable and autonomous.
Through real-world cases, you will examine risks and threats including deepfake fraud, prompt injection, model extraction, Shadow AI, and attacks on AI systems. You will also explore governance frameworks, including ISO 42001, the Secure AI Framework (SAIF), and AIUC-1, as well as emerging AI regulations and their implications for organizations.
This course is ideal for:
- Strategic decision-makers and functional managers integrating AI into their organizations.
- Security and technical professionals translating AI threats into business risks and decisions.
- Legal, risk, and compliance professionals navigating AI governance and regulation.
- Product and engineering professionals developing or deploying AI-enabled products and systems.
- Human resources and operations professionals addressing the organizational, ethical, and legal implications of AI.
Whether you are deciding how AI should be used, managing its adoption, or contributing to AI-enabled products and systems, this course will help you recognize emerging risks, evaluate the controls and governance approaches available to manage them, and make more informed decisions about AI adoption, security, and governance.
Learners who successfully complete all course requirements are eligible to earn a certificate of completion.
Note: Learners who enrolled through the CYBER26 promotion may purchase an optional certificate for $20 upon course completion.
Course Prerequisites
There are no prerequisites for this course.
This course provides the technical context needed to understand the cybersecurity and governance risks associated with generative and agentic AI.
What You Get
1-year access to your course
Revisit content anytime for 1-year from the date you enroll.
Earn a certificate
Earn a Columbia+ certificate upon completion.
Global network of peers
Connect with like-minded learners from around the world.
Expert-led instruction
Learn from Columbia faculty and industry practitioners.
What You Will Learn
Throughout the course, you will connect lessons from major cybersecurity breaches to the emerging risks posed by generative and agentic AI. You will examine how these technologies are changing the threat landscape and explore the governance frameworks, regulatory requirements, and safeguards organizations can use to manage AI risk.
By the end of the course, you will be able to:
- Identify recurring managerial and technical causes of major cybersecurity breaches and apply those patterns to AI-specific vulnerabilities.
- Assess the expanded attack surface created by generative and agentic AI, including prompt injection, model extraction, deepfake fraud, and Shadow AI.
- Evaluate AI governance frameworks and connect them to operational controls across the AI lifecycle.
- Assess organizational exposure to applicable AI regulations and identify where personal and corporate liability may arise.
- Apply governance approaches including AI Bills of Materials, human-in-the-loop safeguards, and regulatory mapping to support informed AI adoption decisions.
- Module 1: Cybersecurity Primer
Review the evolution of cybersecurity and the recurring patterns behind major data breaches.
- Describe how cybersecurity threats and defenses have evolved over time.
- Explain how supply chain vulnerabilities and weaknesses in multi-factor authentication can contribute to major data breaches.
- Compare major breaches involving Target, JPMorgan Chase, and the Office of Personnel Management to identify recurring patterns.
- Module 2: AI Primer
Build foundational context by following the evolution of artificial intelligence from early rule-based systems to modern generative AI.
- Trace major developments in AI from early rule-based systems to modern generative AI.
- Differentiate machine learning from traditional rule-based approaches based on learning patterns from data.
- Associate developments such as neural networks, transformer architecture, and landmark AI applications with the advancement of modern AI.
- Module 3: Multimodal GenAI Risks
Examine how generative AI creates new risks across text, audio, video, and other AI-enabled systems.
- Illustrate how generative AI can create deceptive content across text, audio, and video.
- Interpret the causes of AI hallucinations, their potential use in misinformation, and mitigations such as retrieval-augmented generation.
- Outline how adversarial attacks can fool AI systems and how human-in-the-loop review, adversarial training, and ensemble methods can mitigate these risks.
- Module 4: Agentic AI Risks
Focus on the security risks associated with increasingly autonomous AI agents and approaches for managing them.
- Classify key risks including Shadow AI, authorization and control hijacking, supply chain and dependency attacks, and alignment faking.
- Justify why increasingly autonomous AI agents require organizational visibility, management, and governance.
- Describe how AI inventories and AI Bills of Materials can help organizations manage Shadow AI and AI supply chain risks.
- Module 5: Breaches on and with AI
Examine AI as a dual-use technology by looking at both attacks on AI systems and the use of AI to attack other systems.
- Distinguish between attacks on AI systems and attacks in which AI systems are used to attack other systems.
- Explain how model extraction attacks can replicate an AI model's functionality and compromise the intellectual property invested in its development.
- Discuss how model distillation can use the outputs of a larger teacher model to create a smaller model with similar capabilities at substantially lower cost.
- Module 6: AI Governance and Regulation
Learn how governance frameworks and regulations can support the responsible and trustworthy use of AI systems.
- Justify why AI governance frameworks can help organizations manage risks associated with the development, deployment, and use of AI systems.
- Compare governance frameworks, including ISO 42001, the Secure AI Framework (SAIF), and the AI risks they address.
- Recognize how AI laws and regulations establish requirements, guidelines, and potential penalties for the use of AI.
- Faculty Spotlight: An Interview with Professor Junfeng Yang
Hear from Professor Junfeng Yang about research spanning machine unlearning, AI security, and AI-generated content detection.
- Explain machine unlearning and its relevance to privacy compliance and the removal of poisoned training data.
- Illustrate how backdoors can be introduced into AI systems during model loading or compilation, independent of the training data itself.
- Evaluate how prompt diversification can improve automated jailbreak discovery and its implications for red-teaming and guardrail design.
Instructors
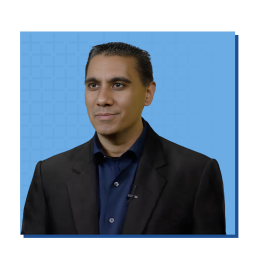
Dr. Neil Daswani is a cybersecurity executive, entrepreneur, investor, author, and Executive-in-Residence at Columbia Engineering. He is also CISO-in-Residence at Firebolt Ventures and Co-Academic Director of Stanford’s Advanced Cybersecurity Program.
Throughout his career, Neil has focused on understanding how systems become vulnerable, how organizations can better manage cybersecurity risk, and how technology can be built more securely. His experience spans organizations including Google, Twitter, LifeLock, Symantec’s Consumer Business Unit, and QuantumScape. He also co-founded Dasient, a cybersecurity company backed by Google Ventures that was later acquired by Twitter, and has served as Chief Information Security Officer at multiple public companies.
Today, his work focuses on both securing artificial intelligence and using AI for cybersecurity applications. He advises multiple venture capital funds and is the co-author of Big Breaches: Cybersecurity Lessons for Everyone and Foundations of Security: What Every Programmer Needs to Know. He holds more than a dozen patents, has published dozens of technical articles, and speaks frequently at leading industry events.
Daswani earned his PhD and MS in Computer Science from Stanford University and a BS in Computer Science with honors and distinction from Columbia University.
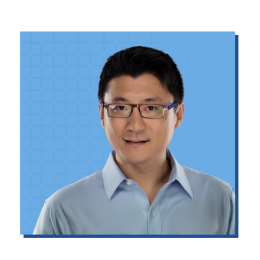
Junfeng Yang is a Professor of Computer Science at Columbia University whose research sits at the intersection of artificial intelligence, security, and software systems. His work addresses critical vulnerabilities and performance bottlenecks in complex computing platforms and has helped drive vulnerability patches and shape engineering practices in systems ranging from Linux to NASA’s Perseverance Mars rover.
Yang is an ACM Fellow and a recipient of the ACM SIGOPS Mark Weiser Award, the IEEE Symposium on Security and Privacy Test-of-Time Award, and an Alfred P. Sloan Research Fellowship.
He earned his PhD and MS in Computer Science from Stanford University and his BS from Tsinghua University.